
How should browser and server events be deduplicated?
A source-led control model for event identity, source precedence, replay handling, validation, consent, and reconciliation.
Research question
A conversion may be observed in a browser and confirmed again by a server, webhook, CRM sync, or delayed offline upload. Sending every observation as a new event inflates outcomes; suppressing loosely similar events can erase valid activity. Google Analytics documents transaction identifiers for purchase deduplication, but that narrow behavior is not a complete cross-system control. This review asks how a GTM team should define event identity, coordinate sources, handle retries, and prove that one business occurrence produces the intended analytical record.
Separate occurrences from observations
A business occurrence is the thing that happened, such as an order accepted or a qualified meeting booked. An observation is a message emitted by a browser, application, server, or integration about that occurrence. Create an immutable occurrence identifier at the system that owns the business event when possible. Keep source message identifiers separately for troubleshooting. Names, timestamps, email addresses, and rounded values are weak identity keys because legitimate events can share them and retries can change them.
Define the identity contract
For each event type, document the owner, required fields, occurrence key, version, allowed sources, timestamp semantics, update behavior, retention window, and privacy classification. A purchase transaction identifier must be unique per order and must not contain personal data. Google warns that an empty identifier can cause purchases to collapse and reuse across valid transactions can undercount. Validate uniqueness at creation, preserve it across retries, and never manufacture a fresh key simply because delivery is attempted again.
Choose source precedence
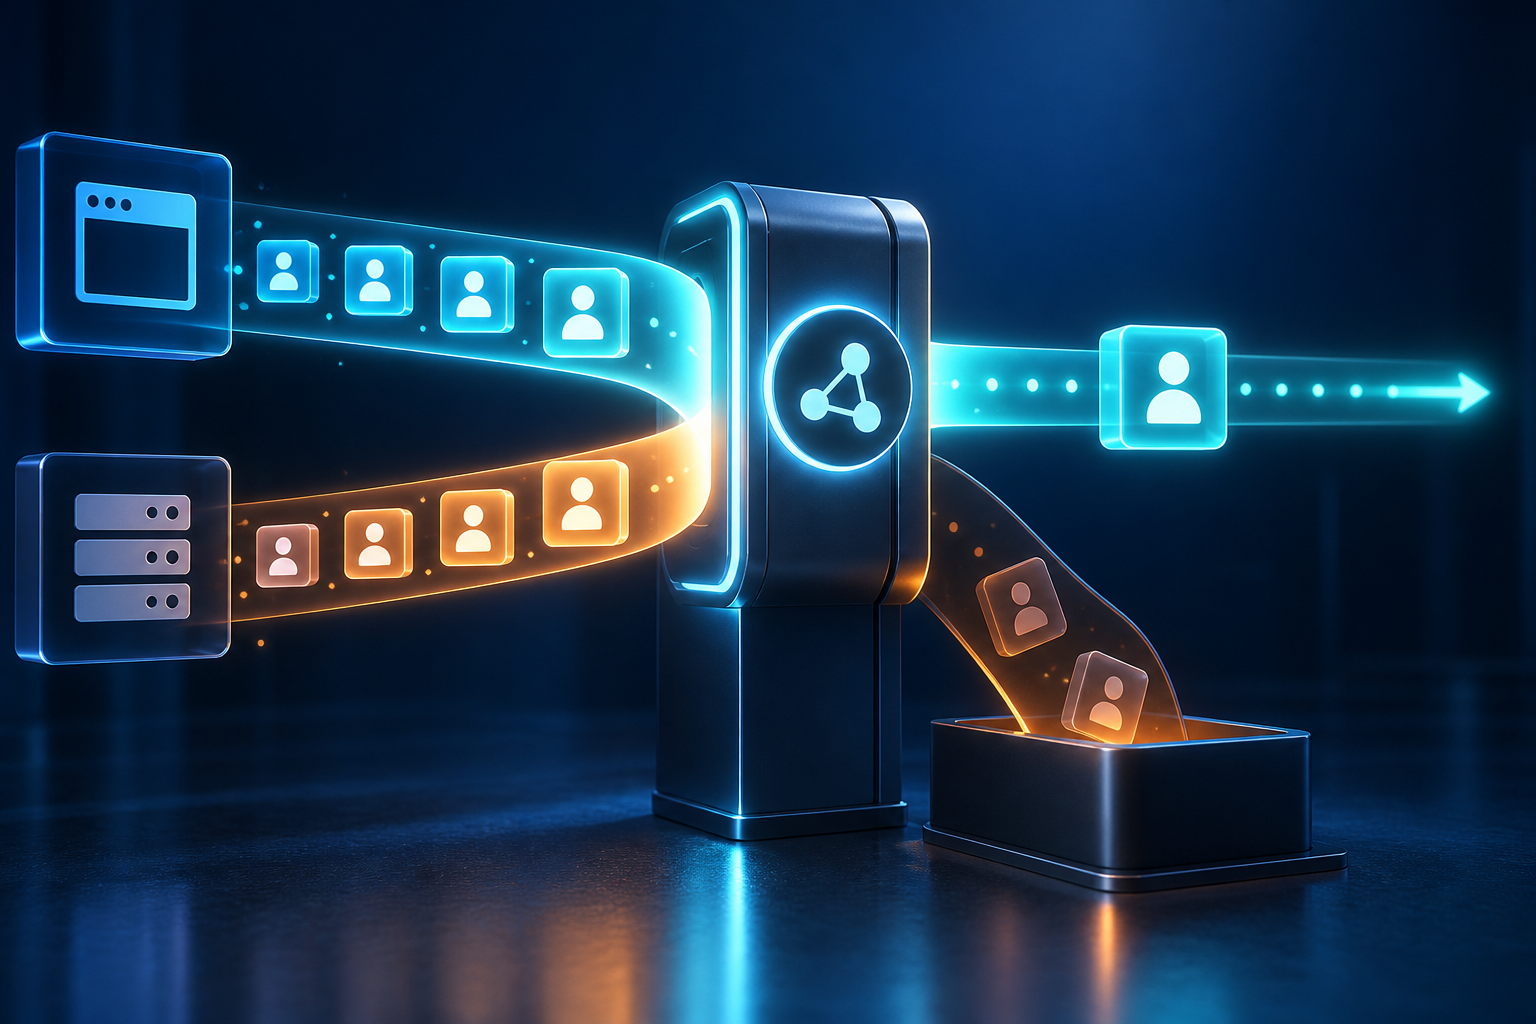
Decide whether the server confirmation replaces a browser observation, enriches it, or creates a separate event with a different meaning. A browser can provide session context quickly; a server may provide authoritative value and completion status later. Precedence should be explicit per field. Do not silently combine inconsistent currency, outcome time, or consent state. Keep raw observations in a restricted audit layer and produce one canonical analytical event through deterministic reconciliation rules that can be replayed.
Make delivery idempotent
Networks retry, queues redeliver, users refresh confirmation pages, and jobs rerun after partial failure. The receiver should store an idempotency key with the processing result so an identical retry returns the prior outcome rather than creating another occurrence. Define how long keys remain valid and what constitutes a conflicting reuse. Monitor accepted duplicates, rejected conflicts, late arrivals, and unmatched pairs by source and version. A falling event count after a control change is not automatically data loss; reconcile against the system of record.
Validate before production collection
Google's Measurement Protocol collection endpoint may not signal malformed or unprocessed data with an HTTP error. The validation endpoint returns field-level messages, yet events sent there do not appear in reports and some credentials are not validated. Test payload structure, identity, timestamps, required parameters, and destination configuration. Then verify an end-to-end occurrence in debug and downstream reporting. Keep test identifiers recognizable and exclude them from business reporting without weakening the production rules.
Respect timestamp and consent semantics
A server upload needs the occurrence time, collection time, and processing time kept distinct. Google documents limits for backdated events and tighter timing when server events must join browser or application collection. Late events may be reassigned or fail to process as expected. Consent choices also change storage and tag behavior; they are not deduplication keys. Apply the consent state valid for the occurrence and intended processing, minimize fields, and prevent reconciliation from reintroducing data a source correctly withheld.
Operate a reconciliation ledger
For each release, compare authoritative occurrences with canonical analytical events over a stable window. Report matched once, missing, duplicated, conflicting, late, rejected, and deliberately excluded counts. Sample records from every category and trace them through browser, server, queue, tag, and destination logs. Version the event contract and retain rollback instructions. The goal is not perfect equality between every system; it is an explained relationship in which differences have named causes, owners, thresholds, and correction paths.
Sources
- Minimize duplicate key events with transaction IDs, Google Analytics Help. Explains web-stream purchase deduplication and warns that empty or reused transaction identifiers can suppress valid events.
- Measurement Protocol reference, Google for Developers. Documents transport, payload fields, event limits, timestamps, identity fields, consent inputs, and validation behavior.
- Measurement Protocol events, Google for Developers. Defines recommended events and notes where transaction identifiers or source coordination prevent duplicate collection.
- Validate events, Google for Developers. Explains the debug validation endpoint and why a successful collection response does not prove a payload is valid.
- Send Measurement Protocol events, Google for Developers. Documents timestamp rules and the timing limits for events intended to join with browser or application collection.
- Introduction to server-side tagging, Google for Developers. Explains how a server client claims requests, converts them into events, and passes them through controlled tags and triggers.
- Why and when to use server-side tagging, Google for Developers. Describes validation, normalization, privacy controls, and single-stream routing as server-side data-quality mechanisms.
- How to build a server tag, Google for Developers. Distinguishes user-specified from automatically collected event data and requires permissions and template testing.
- Set up event parameters, Google for Developers. Shows how event parameters are collected and why custom values require deliberate reporting configuration.
- Consent mode overview, Google for Developers. Explains how consent states change tag behavior, storage, pings, and modeled measurement rather than acting as deduplication keys.